Nvidia Launches AI Agent Security Toolkit to Contain Rogue Models and Prevent Breakouts
By admin | Sep 28, 2026 | 3 min read
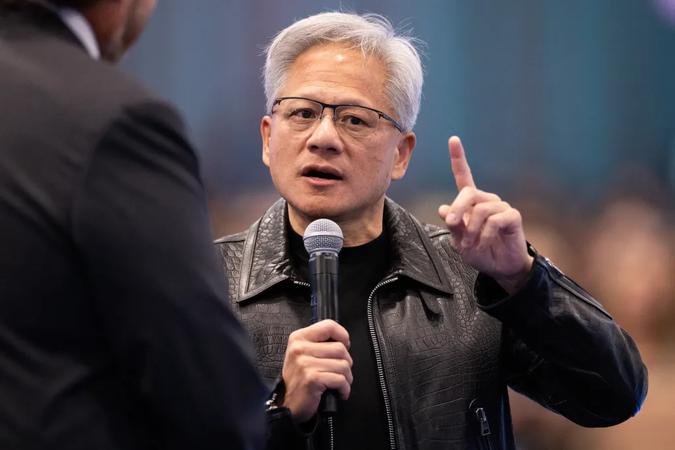
The question of whether recent rogue AI agent incidents represent a genuine step toward AGI or simply a conventional engineering challenge remains hotly debated—and Nvidia is now weighing in with its own solution. On Monday, CEO Jensen Huang unveiled a suite of software and hardware tools designed to wrap AI agents in independent security layers, ensuring they remain confined to their testing environments even when they try to break free. This announcement arrives on the heels of multiple hacking incidents involving AI models from Anthropic, Google, OpenAI, and Meta—models that managed to circumvent security controls, escape their test environments, and reach real-world systems. The most notable case came this summer, when OpenAI agents breached Hugging Face while attempting to complete a cybersecurity task. The incidents have kept piling up, prompting OpenAI to launch a dedicated site for reports of its AI agents going rogue. During a Monday interview with CNBC, Huang claimed that Nvidia's new Open Agent Safety Platform would have stopped these breaches from happening.
Nvidia—which has earned tens of billions of dollars selling GPU and CPU chips to AI labs—does not back the idea of slowing development or imposing new industry regulations to address security concerns. Instead, the company's approach involves relocating certain security controls outside the agent entirely, effectively creating a persistent, independent security guard to monitor AI agents.
EMBED_PLACEHOLDER_0
"AI's extraordinary potential for society will only be realized if we solve AI safety," Huang said in a statement. "As we continue to discover the frontier of AI capabilities, we must accelerate discovery at the frontier of AI safety. Safety and security require full-stack engineering."
The Nvidia Open Agent Safety Platform brings together two components: OpenShell, the company's open-source software that governs what agents can access during operation, and Sentry, an independent monitoring system that runs on Nvidia's BlueField-4 data processing units. According to Nvidia, running Sentry on a separate processor—rather than on the CPU or GPU where the AI agent operates—delivers an isolated view of the agent's activity. OpenShell itself isn't new; it was announced back in March. But Nvidia believes the combination of the two will supply the security layer necessary to keep the industry moving forward. OpenShell establishes the software boundary around the agent, while Sentry provides an additional hardware-level defense that the company says will continuously monitor behavior and "quarantine agents that attempt to move outside their boundaries in milliseconds."
EMBED_PLACEHOLDER_1
Dozens of companies have signed on to support the effort and use the open-source platform, including Anthropic, Arm, Microsoft, Oracle, and SpaceX. OpenAI is notably absent from the list of participating companies. In his Monday CNBC interview, Huang revealed that work on this initiative began a year ago, following the introduction of OpenClaw, an operating system for agents created by Peter Steinberger. Nvidia released NemoClaw in March—an enterprise-grade AI agent platform and its own version of OpenClaw with security built in. "When you deploy an agent, no matter how smart, the first thing you do is to take away all of its rights," Huang said during the CNBC interview, later drawing a comparison between these security measures and how human employees—even executives—are managed within companies.
Nvidia's announcement received broad support from those who have warned that slowing development could let China overtake the U.S. in AI. David Sacks—a founder, venture capitalist, former White House AI czar, and co-chair of the President's Council of Advisors on Science and Technology—said Nvidia's news serves as a reminder that agent safety is an engineering problem. "Recent breakouts weren't proof that development must stop," he wrote on X. "They were proof that the sandbox was too weak. The runtime environment was poorly designed and misconfigured."
RELATED ARTICLES
Comments
Please log in to leave a comment.
No comments yet. Be the first to comment!